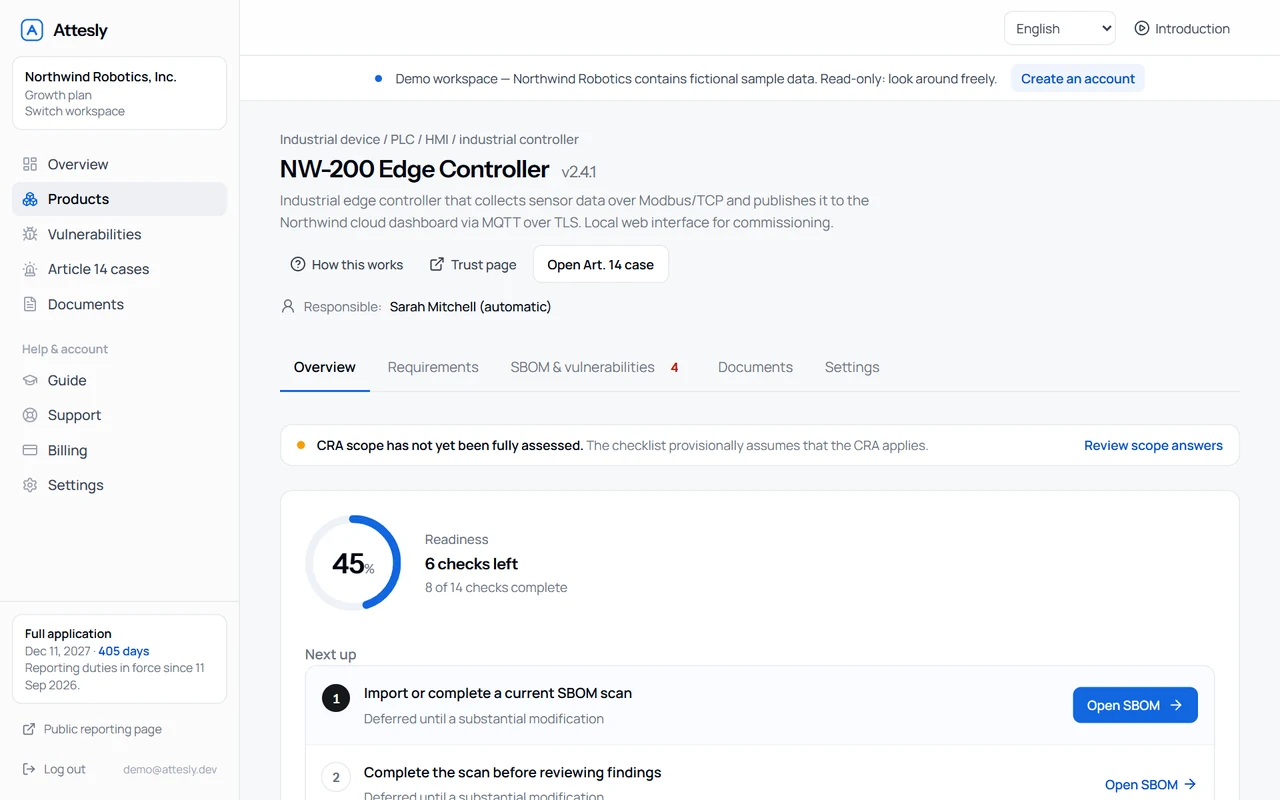
Import your SBOM.
Keep components in the product record and review the imported data.
Turn SBOMs, vulnerabilities and security reports into a traceable work list. Your team reviews saved assessment drafts, deliberately opens a confirmed case and tracks its deadlines.
For businesses in the United States
Attesly works with the formats and sources your team already uses:
CycloneDX, SPDX, CSV, OSV, NVD, EU 2024/2847, Art. 14, Annex VII, REST-API
Add your product and import its component list. Attesly links known vulnerabilities to the product record and shows the next review steps. External security reports are saved as assessment drafts; your team decides whether to open a reporting case.
If you currently keep scan reports, spreadsheets and documents apart, Attesly brings tasks, owners, deadlines and documents together for each product. Setup guidance and support are available directly in the app.
Keep components in the product record and review the imported data.
New critical findings are saved for review; a team alert points to new work.
Inspect external security reports and critical findings as assessment drafts. Your team makes the judgment.
Deliberately open a case, record the awareness time and track its deadlines. Record awareness in your local time zone; Attesly stores the exact instant.
No setup fee, cancel anytime and a 30-day money-back guarantee. The first invoice equals one month’s fee.
Article 14 steps show the due date for the 24-hour early warning and the 72-hour notification.
Your components are rechecked against OSV every day. Critical findings and due deadlines arrive as alert emails.
Keep templates and product evidence together. Your team reviews and approves.
Every plan includes the core CRA compliance workflow. Bigger plans add products and API access.
Upload CycloneDX, SPDX or CSV – or, from Growth, push SBOMs straight from your CI through the API.
VulnerabilitiesEvery component is rechecked daily; components that carry a CPE are checked against the NVD.
Article 14The 24-hour early warning and the 72-hour notification, prepared with a due date for every step.
Annex VIISix document templates for your CRA records. Complete the details, attach evidence and review them with your team.
PublicA public page for your products and an intake form for researchers to report vulnerabilities.
NotificationsVulnerability reports, critical findings and due deadlines reach your team straight away.
SourcesChanges to official CRA sources show up in the dashboard, so your record stays current.
Roles and classes
The Regulation binds everyone who brings a product with digital elements to the EU market. Most of the weight sits with the manufacturer.
Actual app screen · sample data · scroll to explore

Film · 54 seconds
With narration and on-screen text · demo data from a fictional company
Live demo
Add products, import an SBOM and try templates with sample data. No email delivery, live vulnerability scans or AI calls. Resets daily.
You save per month
Estimate$2,675
Net of the Starter plan price
Pays for itself in ~2 months.
An estimate from your inputs and typical figures — not a guarantee. Year one. “With Attesly” includes the Starter plan ($6,000 a year, 12 monthly invoices), keeps 45% of the documentation hours and half of the consulting days. Payback: the plan’s yearly price, divided by the saving before the plan price spread evenly over twelve months. Saving / plan cost: that saving divided by the plan price (a benefit-cost ratio, not net ROI). Later years: $10,575 without a system, $10,860 with Attesly. Possible fines are left out.
30-day money-back guarantee
Guarantee termsSecure checkout via Stripe
for businesses only
One product family, documented properly
No setup fee. Cancel anytime.
A portfolio with releases every month
No setup fee. Cancel anytime.
Many product lines, several brands
No setup fee. Cancel anytime.
Up to 150 products, order online
No setup fee. Cancel anytime.
FAQ
Practical preparation for the people who keep a product’s compliance record: Article 14 reporting, SBOMs and the evidence behind the technical file.
Questions, RFPs or requirements lists? We’ll get back to you personally.
Fill out the form or
Fabian LorenzFounder · Neithra Technologies
Thirteen years in the German police shaped how we work: careful documentation, transparent decisions and discretion with data.